Quick start#
Pencils up. Five minutes, one command, a mark sheet: install PROCTOR, run the first check, read what the proctor saw.
-
Add PROCTOR to the app as a dev dependency.
composer require waynestate/proctor --devExpected: Composer installs it, and the command is then
vendor/bin/proctor. -
Run the first check.
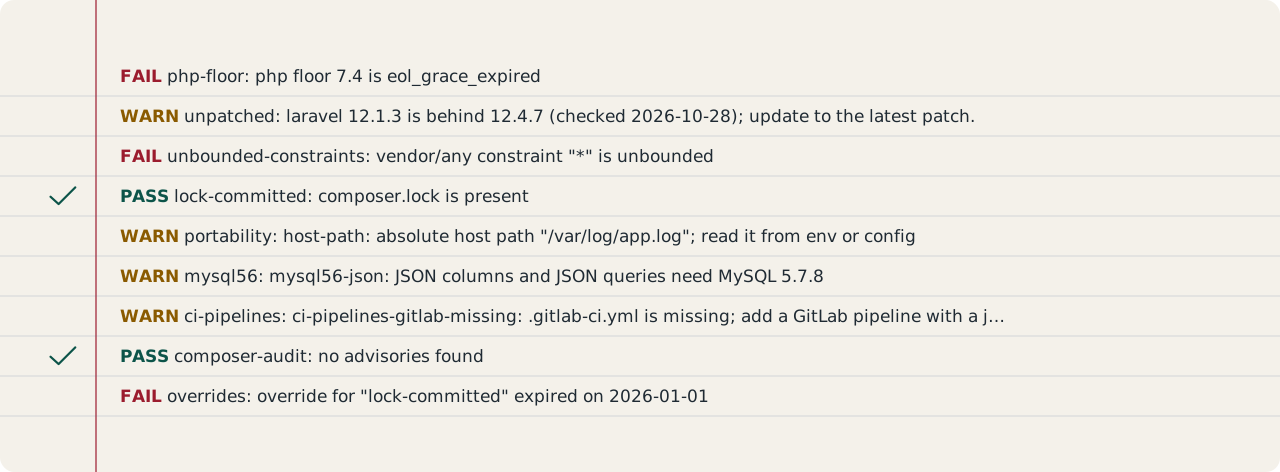
vendor/bin/proctor checkExpected: the text report. A header line with the tool and the composer version, a line naming the policy in use, one line per finding written in words, then a RESULT line. Exit 0 when nothing failed (warnings allowed), 1 when something did.
-
Read the mark sheet.
Every finding carries a stable, namespaced rule id:
proctor/<check-id>for a check's default finding,proctor/<check-id>/<rule>for a named rule. A FAIL is a resit; a WARN is a note in the margin; an INFO is the proctor thinking out loud. -
Make the run deterministic.
vendor/bin/proctor check --today=2026-01-01 --php-runtime=8.4.0Expected: the same marks on every run.
--todayoverrides today's date so runs are deterministic, and--php-runtimetells theunpatchedcheck the PHP version that will serve the app. CI should pass the deploy image's PHP, not the runner's. -
Emit a machine-readable mark sheet (optional).
vendor/bin/proctor check --format=jsonUse
--format=codequalityfor GitLab's Code Quality JSON, or--format=sariffor a SARIF 2.1.0 log that GitHub code scanning can read. -
Name the policy explicitly (optional).
vendor/bin/proctor check --policy=policy.jsonWithout
--policy, PROCTOR resolves the policy in this order: thePROCTOR_POLICYenvironment variable, the app'svendor/waynestate/creed/policy/policy.json, then the copy bundled with PROCTOR.
What you built#
You ran PROCTOR's first marking pass: a verdict per check against the CREED policy, with an exit code CI can gate on. Nothing in the app changed; the proctor only watches.
Next steps#
- Install: requirements and the single-file PHAR route for apps without Composer access.
- Reference: commands: the long-form docs for the commands, rule ids and exit codes.
- When you are ready for CI, the README's GitHub code scanning section shows a workflow that runs the check with
--format=sarifand uploads the log to code scanning.